ITAR Compliance in Electronics Supply Chains: What Buyers Must Verify
For procurement, engineering, operations, and quality leaders in aerospace and defense-adjacent sectors, establishing an electronics supply chain involves far more than assessing unit cost, surface-mount technology line speed, or factory capacity. When printed circuit board assemblies govern mission-critical guidance systems, flight controls, or tactical communications, compliance with the International Traffic in Arms Regulations (ITAR) becomes a vital operational threshold.
A critical distinction must be drawn immediately: ITAR registration with the Directorate of Defense Trade Controls (DDTC) does not represent government approval, program authorization, or an official product certification. Registration is a statutory administrative baseline. Genuine ITAR compliance is an ongoing, operational discipline that dictates how an electronic manufacturing services (EMS) partner governs data security, controls physical and logical access, qualifies tier-two suppliers, and preserves production traceability. Below is a practical verification guide detailing the controls buyers must examine across high-reliability electronics manufacturing.
1. Technical Data Handling and Digital Safeguards
Under ITAR, technical data includes blueprints, schematics, engineering designs, bill of materials (BOM) files, and computer-aided manufacturing data required for defense articles listed on the United States Munitions List (USML). Improper digital transmission or uncontrolled server storage constitutes an unauthorized export.
A compliant contract manufacturer must treat data handling as an audited operational pipeline. Buyers should verify the protocols safeguarding their files before transmitting a single Gerber or CAD package.
Buyer Verification Questions
- Access Control: Are your design files, firmware, and fabrication drawings isolated within role-based access environments, or are they accessible to general staff across your IT network?
- Encryption Standards: Are customer engineering packages protected by end-to-end encryption both at rest and in transit using protocols compliant with NIST standards?
- Logical Boundary Integrity: Does the EMS provider maintain separated physical or virtual server architectures to prevent inadvertent cross-contamination between commercial and export-controlled projects?
2. Personnel Controls and On-Site Access
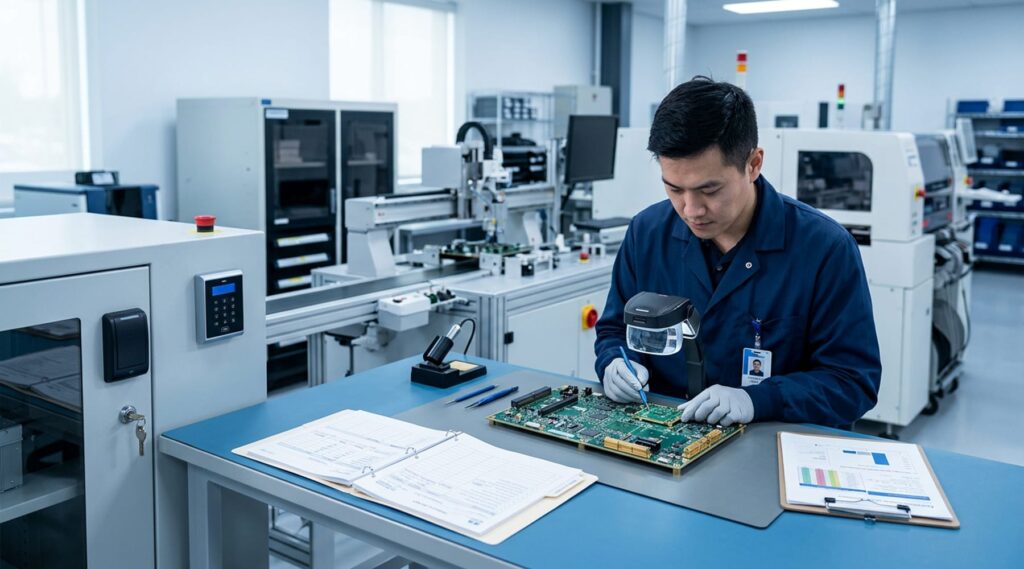
Physical plant access forms a core pillar of ITAR enforcement. The regulations govern disclosures to foreign persons within the borders of the United States. In an electronics assembly environment, visual access to engineering drawings, specialized fixturing, work instructions, or partially populated boards qualifies as a technical data transfer.
Procurement teams must inspect how an electronics manufacturer operationalizes identity verification on the factory floor.
Buyer Verification Questions
- U.S. Person Verification: What standard operating procedure governs the verification and recurring validation of U.S. person status (U.S. citizens and lawful permanent residents) for line operators, process engineers, rework technicians, and quality inspectors?
- Visitor and Vendor Protocols: How are maintenance technicians, equipment vendors, and unvetted visitors managed within production areas handling controlled assemblies? Are badge controls, physical escort logs, and visual redaction policies consistently enforced?
- Secure Floor Segregation: Does the facility utilize physical barriers, locked assembly bays, or restricted-access surface-mount lines when processing controlled high-reliability runs?
3. Upstream Supplier Oversight and Sub-Tier Traceability
An electronic assembly is only as compliant as its lowest-tier component. Surface-mount components, bare rigid-flex boards, specialized conformal coatings, and custom mechanical enclosures travel through extensive supply chains before reaching the final pick-and-place lines. If an unvetted vendor receives controlled drawings to quote a custom heatsink or fabricate an advanced substrate, compliance is compromised.
OEMs require full visibility into how their EMS provider vets, manages, and audits lower-tier suppliers.
Buyer Verification Questions
- Flow-Down Mechanisms: How are export control clauses, data security requirements, and NDA provisions formally flowed down into purchase orders with custom component fabricators?
- Counterfeit Mitigation Systems: What authentication procedures and incoming inspection protocols prevent grey-market or counterfeit electronic parts from entering the defense supply chain?
- Approved Vendor Lists (AVL): Does the manufacturer maintain documented qualification procedures for bare-board fabricators, testing labs, and component distributors supporting regulated builds?
4. Production Documentation and Work Instructions
In high-reliability electronics, documentation is inseparable from the hardware itself. Under ITAR, assembly travelers, rework slips, automated optical inspection (AOI) logs, and test procedures frequently contain controlled parameters. If an assembly traveler contains a schematic excerpt, it requires the same export control safeguards as the primary drawing.
Buyers must ensure that the manufacturer’s documentation cycle protects information while maintaining complete lot traceability.
Buyer Verification Questions
- Traveler and Work Instruction Labeling: Are physical build books, travelers, and electronic work instructions marked with appropriate export control warning statements?
- Traceability and Record Retention: Does the manufacturing execution system (MES) store traceability records, lot numbers, test data, and component serial numbers securely for the full statutory retention periods required by regulations and program contracts?
- Scrap Disposal Controls: How are rejected boards, misprinted stencils, trimmed leads, and damaged subassemblies destroyed or disposed of to prevent unauthorized recovery or data disclosure?
Summary Checklist: What Procurement Must Demand
Before issuing a request for quotation (RFQ) or transferring proprietary design files, verify these core competencies:
- Valid, current DDTC registration documentation (acknowledged as administrative registration, not a government endorsement).
- A documented Technology Control Plan (TCP) that spells out physical, logical, and personnel procedures.
- Certified quality management architectures such as AS9100D or ISO 9001 that standardize process controls, lot tracking, and preventive risk analysis.
- Formal employee training regimens on export controls and data protection protocols.
- Secure transfer mechanisms for quote packages, design reviews, and engineering change orders.
Notice: Regulatory compliance requirements vary significantly depending on product classification, end-use, and prime contract requirements. Buyers should always confirm their exact compliance obligations with qualified legal or export-control counsel before initiating manufacturing partnerships.
Strengthen Your Domestic Supply Chain with American Precision Electronics
Maintaining defense-grade reliability demands rigorous quality management, uncompromising data protection, and a trusted domestic partner. Operating from our 30,000-square-foot facility in Illinois, American Precision Electronics combines advanced surface-mount assembly with the rigorous oversight, technical precision, and physical control required by high-reliability OEMs. We operate with strict adherence to domestic manufacturing standards, continuous process improvement, and end-to-end data integrity.
Contact American Precision Electronics today to discuss your high-reliability manufacturing requirements and review our quality frameworks.